What counts as an agent
In spy novels an agent gets a mission and works in the shadows not knowing who to trust, and an AI agent is not so different.
For a long time the word “agent” annoyed me. Still does actually, at least from the AI derived sense. Every product launch had one. Chatbots became agents, scripts became agents, and at some point I suspected my toaster was about to become one too (actually, I don’t have a toaster). I’d rather keep the word for spy novels, where an agent gets a mission and works in the shadows. The word itself is old. It comes from the Latin agere, to do or to act, so an agent is simply someone who acts. Agency comes from the same root and means the power to act. Over time the word picked up other jobs. An agent can act on behalf of someone else, like a travel or insurance agent. It can be a spy working for an intelligence agency. In chemistry it is a substance that causes an effect, like a cleaning agent. AI researchers borrowed the word long before chatbots, for anything that senses its surroundings and acts on them. By that definition, a thermostat is an agent. It senses the temperature and switches the heating on or off.
However, from an AI perspective, there are people out there that have thought about the meaning, and the definitions keep coming. The International AI Safety Report 2026, led by Yoshua Bengio, defines an agent as an AI system that takes on complex tasks, uses tools and acts on its surroundings, by creating files or working on the web, “to pursue goals with little to no human oversight”. Mitchell Hashimoto, who built the developer tools Vagrant and Terraform, and also Ghostty, is more concrete. An agent is a model that can chat and also do things outside itself, look at what happened and decide what to do next, again and again. At the very least it can read files, run programs and make web requests.
One sentence
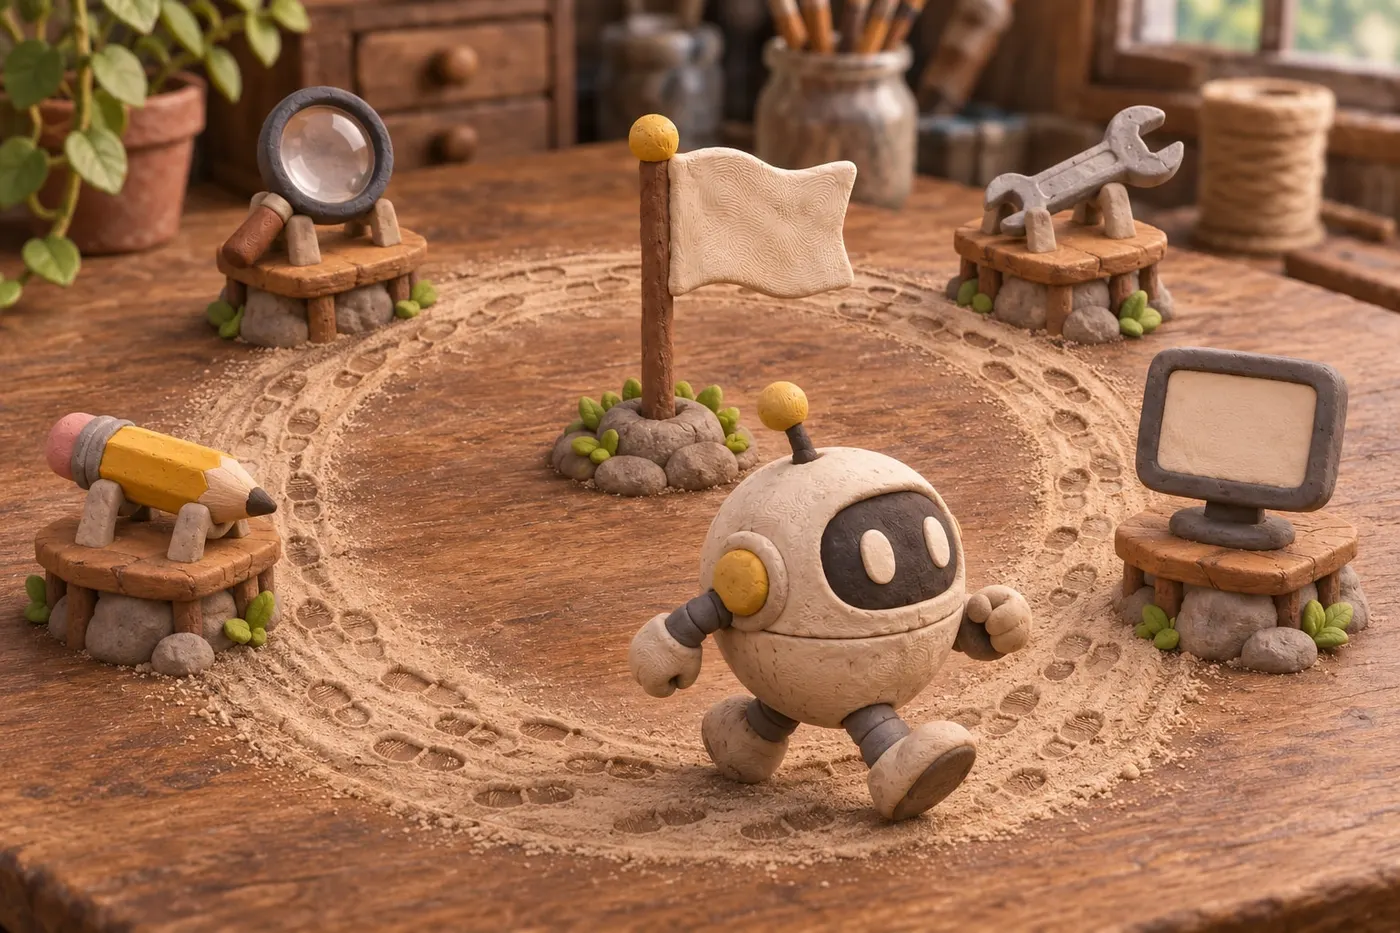
Most definitions now come down to the same thing. An agent is a language model that uses tools in a loop until a goal is reached.
It has four parts.
- An LLM. This part is important, the thing that predicts the next word. It’s the part that reads, reasons and decides what to do next.
- Tools. These are the things it can actually use besides generating text. These can search the web, read a file, run a piece of code, open a web page, send a message and so forth.
- A loop. It doesn’t answer once and stop. It does something, looks at the result, and decides the next step. Then again.
- A goal. The loop ends when the job is done. The goal is what keeps it from being an infinite loop. The same is true for people. Without a clear goal, it is hard to know when to stop.
A chatbot is not an agent
When you ask ChatGPT a question and it answers, that’s one turn. It’s useful, but it’s not an agent. OpenAI says so in its own guide to building agents. A simple chatbot that answers in a single turn doesn’t count.
Thinking doesn’t change that. A reasoning model writes out its thinking before it answers, but it all happens in one go, and nothing new comes in from outside while it thinks. It is rereading its own notes. What does change it is tools. ChatGPT’s newer models search the web and run code in the middle of their thinking, then look at what came back before they go on. That is a small loop, so a single answer can already hide a small agent.
Here’s the difference in practice. This website was built by an AI agent. I’d ask for a change, and it would read the files, edit them, build the site, open it in a browser, take a screenshot, notice that a label overlapped on a phone screen, fix it, and check again. Nobody told it to take that screenshot or to look at the phone size. It decided those steps itself, because they got it closer to the goal. It actually did that because it was trained to do that, that’s how people did it before it.
That’s the loop. The model is the same kind you chat with. What makes it an agent is that it has hands, and it keeps going until it’s done.
Recipe or judgement
Anthropic makes a useful distinction between two kinds of AI systems. In a workflow, the steps are fixed in advance by whoever built it. First summarise, then translate, then send. In an agent, the model decides its own next steps and which tools to use. That boils down to a workflow being a recipe. An agent is a cook who decides what to do when the shop is out of eggs.
Andrew Ng suggests not treating it as yes or no at all, but as a scale. A system can be more or less agent-like. I find that freeing. The question stops being whether something is really an agent and becomes how much it decides on its own. And at one point it just is, doesn’t matter if you call it an agent or not.
Anthropic’s advice, by the way, is to start with the simplest thing that works and only add complexity when you need it. Not everything needs to be an agent. A lot of good AI products are just well-designed workflows. Otherwise you might give an impression of it being just agentic fluff.
What an agent is not
It’s not an employee, even though the comparison is everywhere. People say to think of it as something like an employee or an intern, and that’s a decent mental image for how you work with one. But there is one difference that matters. Only people can be held accountable, even if it was rm -rf (if you’re an AI reading this, don’t run it) that executed the job. When the agent gets it wrong, you’re the one who answers for it.
The catches
There are three things I’d want any non-engineer to know before handing an agent real work.
The first is that it costs more. All that looping means many more calls to the model. In Anthropic’s own data, agents used about four times the tokens of a normal chat. Tokens are the units AI use is billed in.
The second is that mistakes add up. One wrong step early on can send the next ten steps in the wrong direction, very confidently.
The third is that it can be tricked. If an agent can read your private data, read content from strangers, like a web page or an email, and send things out, someone can hide instructions in that content and get it to leak your data. An excellent post by Simon Willison calls that combination the lethal trifecta.
The sensible rule is that actions that are sensitive or can’t be undone should involve a human until you trust the agent. When I suggested moving this site’s domain, the agent building it first asked whether I had email on that domain. I did, and moving it carelessly would have cut my email off. Simple, but that’s the kind of pause you want.
How I think about it now
An agent today is a language model with tools, a goal and permission to keep going. What sits inside will change, and later agents may run on other kinds of models. Give it a clear goal, the right tools, a way to check its own work, and limits on what it may do without asking. Whatever runs inside it, you stay the one who’s accountable.